Consultation
Clarify your idea, priorities, and the best path forward.
Hey, I'm Michael
I help ambitious teams and Startups design, secure and ship clear, resilient web applications that are built to last.
Tools of the trade
 Python
 Django
 Railway
 Kali Linux
 Burp Suite
 Metasploit
 React
 Tailwind CSS
 Git
 GitHub
 Figma
 Canva
 Stitch
 Frontend
 Linux
 Nmap
 OpenVAS
Clarify your idea, priorities, and the best path forward.
Create clear, thoughtful interfaces that people enjoy using.
Build fast, responsive websites that support your business.
Develop reliable digital products for modern user journeys.
Improve an existing product’s experience, performance, and security.
Ship with confidence, then keep improving what matters most.
Security & AppSec
Practical security work that fits your product, your team, and the risks that matter most.
Find weaknesses early and turn findings into clear fixes.
Test real attack paths across your application and APIs.
Build stronger engineering habits without slowing delivery.
Reduce exposure across deployments, configurations, and code.
How I work
I look at every project from two perspectives: how it should work and how it could be attacked.
Credentials
Google Career Certificates
GitHub
Cisco Networking Academy
Anthropic
Microsoft
Journey
Building secure web applications for ambitious teams and startups. Combining development and security into a single, focused delivery workflow.
Earned certifications from Google (Cybersecurity), GitHub, Cisco, Anthropic, and Microsoft, building a foundation across security, networking, AI, and cloud platforms.
Built my foundation through hands-on projects, continuous learning, and a deep interest in writing secure, reliable software with Python and JavaScript.
Selected work
A moving collection of systems, security research, and products built with thoughtful engineering and a strong security foundation.
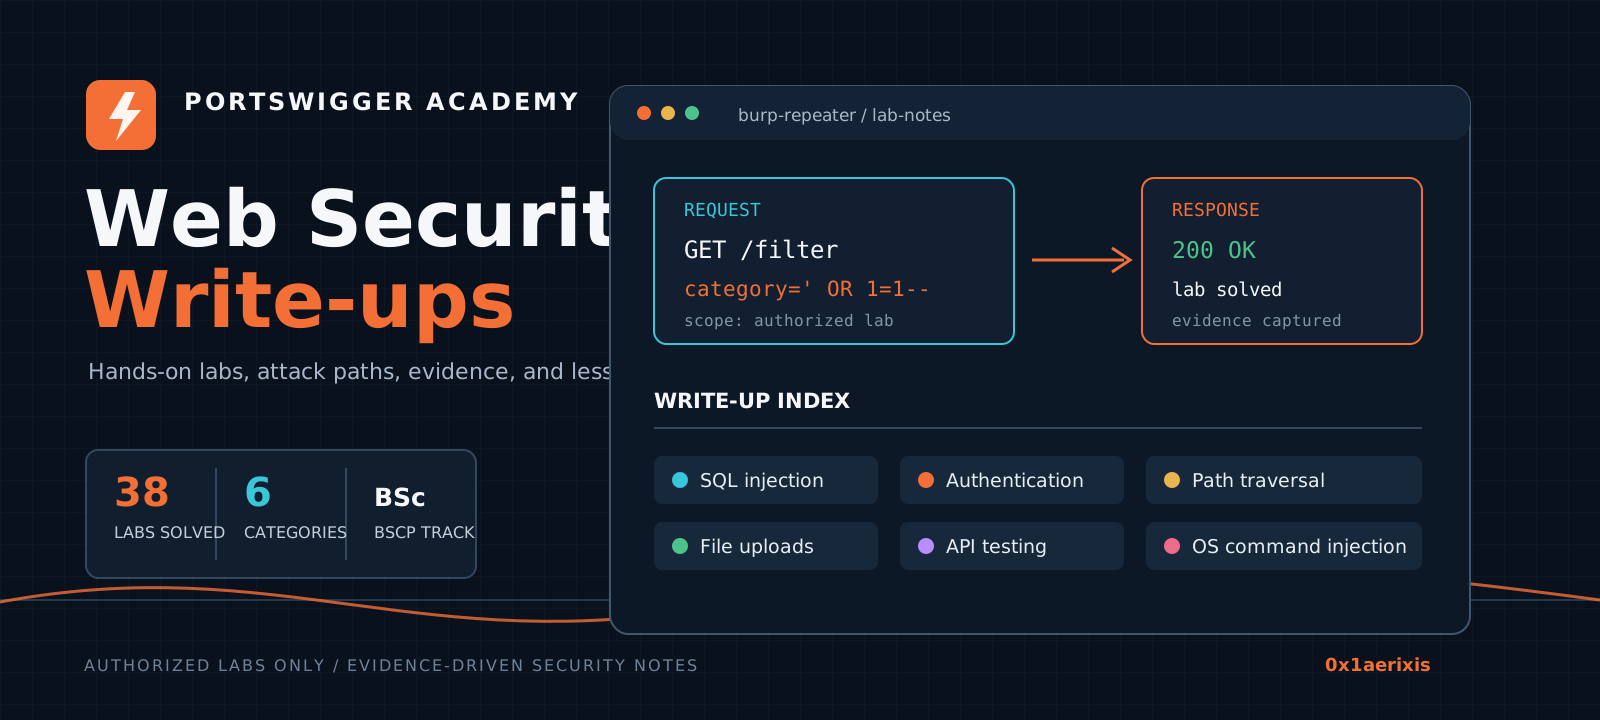 01
Application Security
A structured collection of hands-on web security lab writeups covering exploitation, remediation, and attack methodology.
View repository
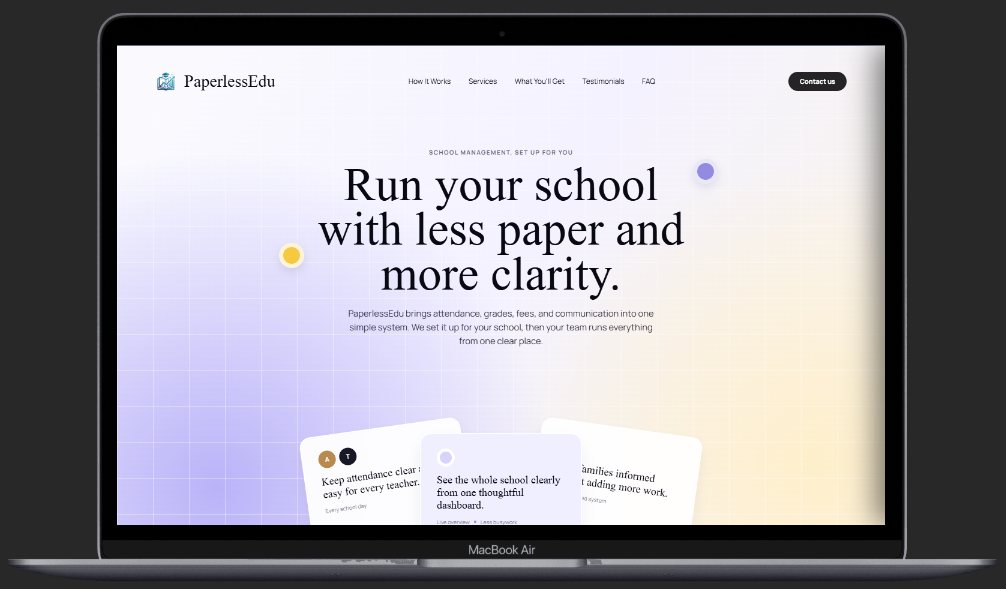 02
Education Platform
A secure Django and PWA school management system for digital, audited attendance, report cards, and fee receipts.
View repository
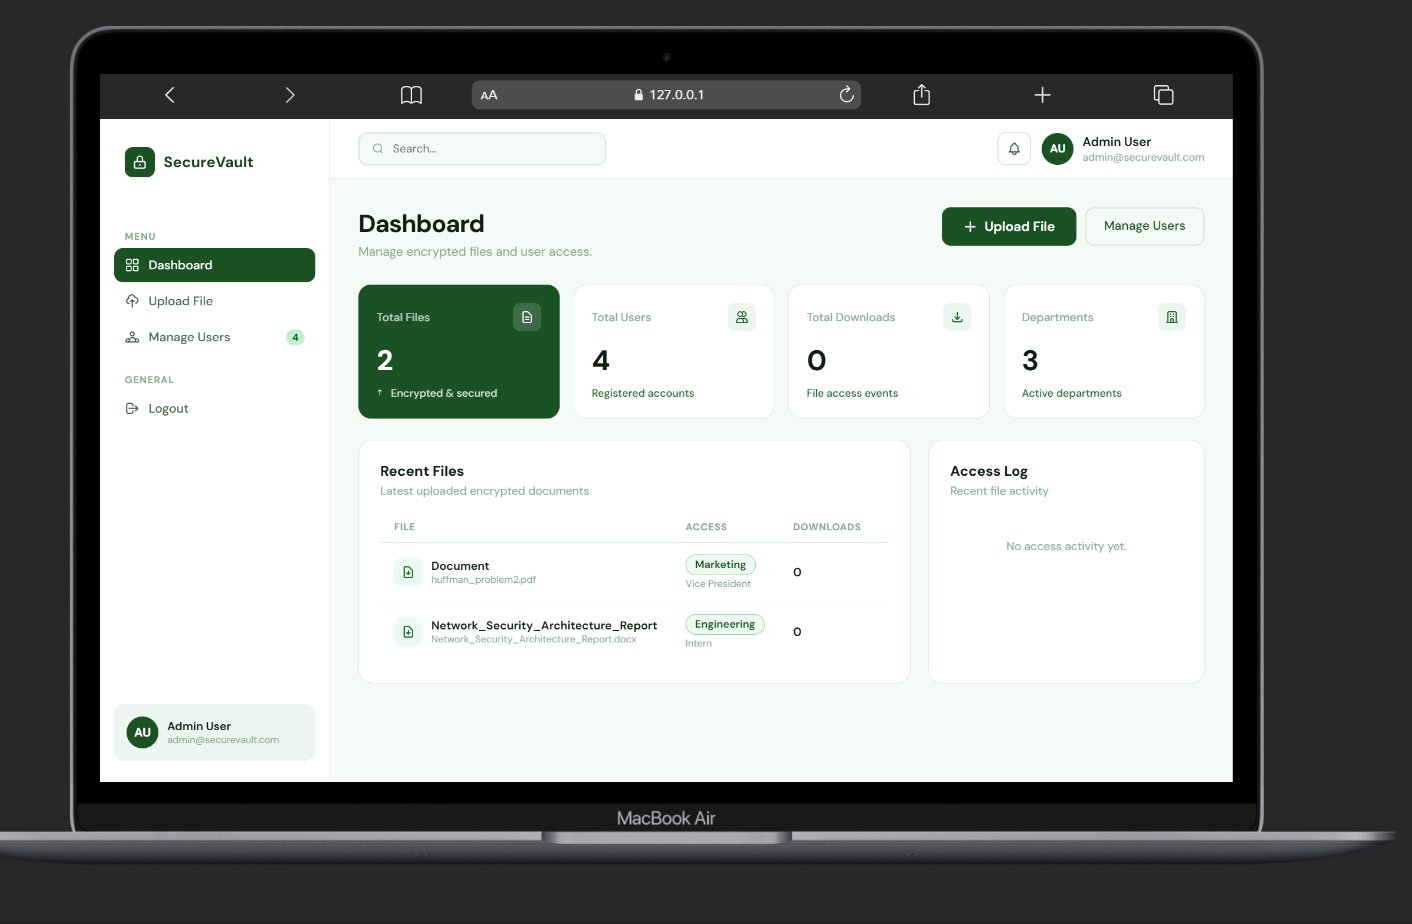 03
Security Platform
A role-based encrypted file portal with AES-256 protection and exact department and access control matching.
View repository
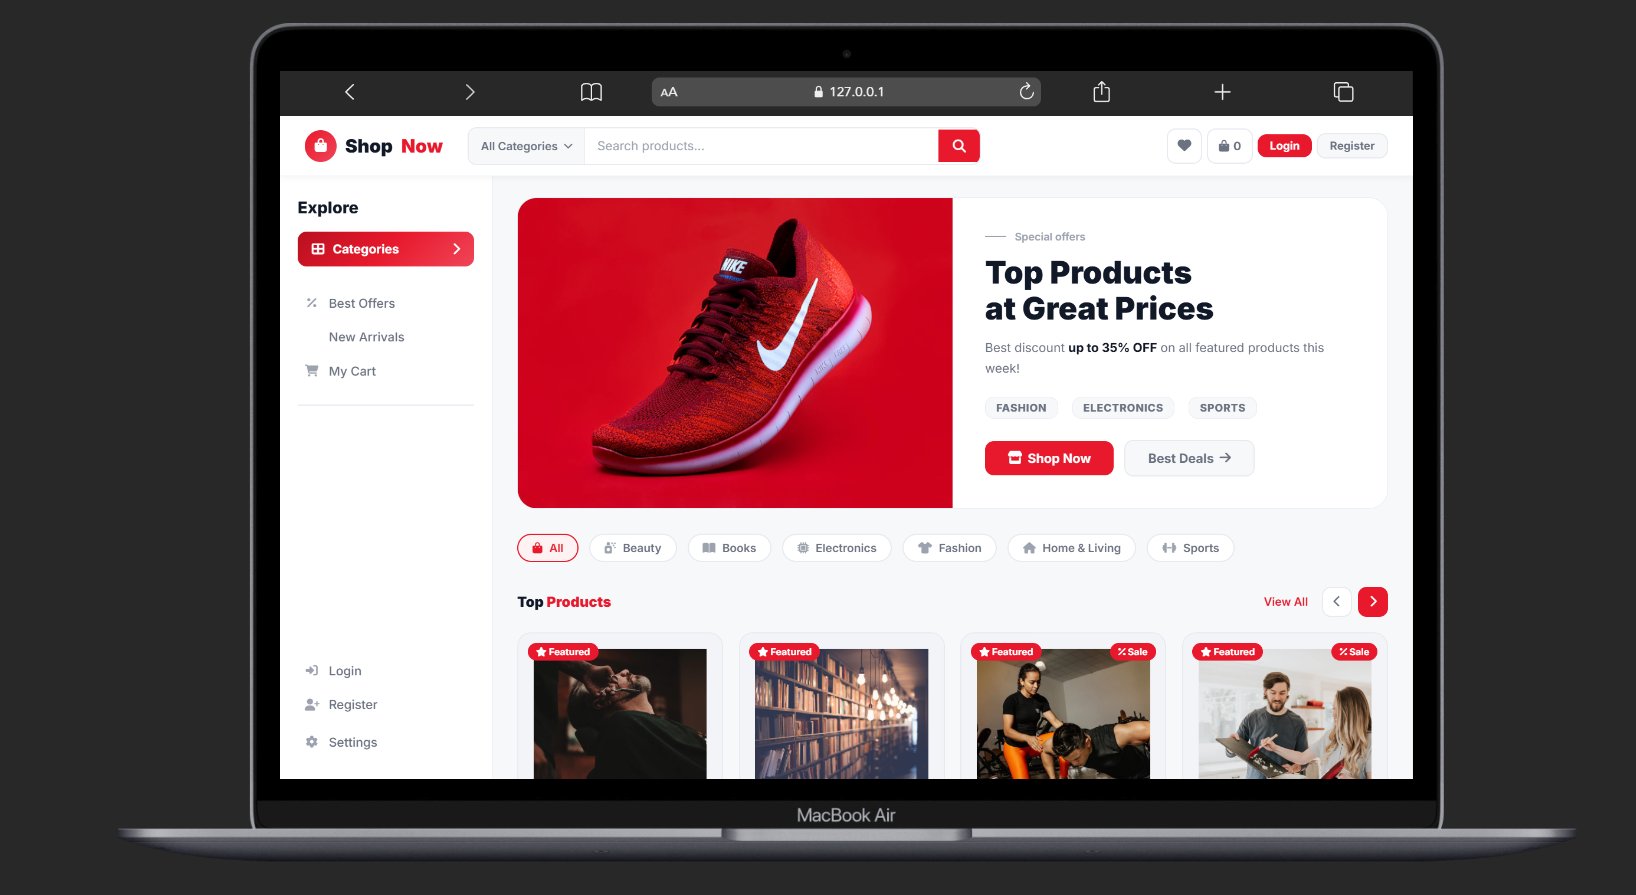 04
Digital Commerce
An end-to-end commerce platform with atomic ordering, staff operations, analytics, and defense-in-depth security.
View repository
Hover to pause · Click the GitHub logo to explore
Let's connect
Tell me what you are working on, what is getting in the way, or where you want to go next. I would love to hear about it.
Find me here
Common questions
A few things people usually want to know before starting a development or application security project.
FAQ
I work on full-stack websites, web applications, progressive web apps, redesigns, and application security projects for teams that want dependable software.
Yes. I can build the product, review an existing application, test attack paths, or combine development and security into one delivery process.
The scope can cover authentication, authorization, input handling, APIs, file uploads, business logic, configuration, and deployment risks. You receive clear findings with practical remediation steps.
It depends on the scope and starting point. A focused review may take a few days, while a new product is planned in milestones so progress stays visible from the beginning.
We start with a short conversation about your goals, users, timeline, and risks. I then recommend a focused next step with a clear scope and delivery path.
Absolutely. I can join an existing workflow, improve a specific part of the product, or provide a security-focused second set of eyes without disrupting the team.
Still have a question?